
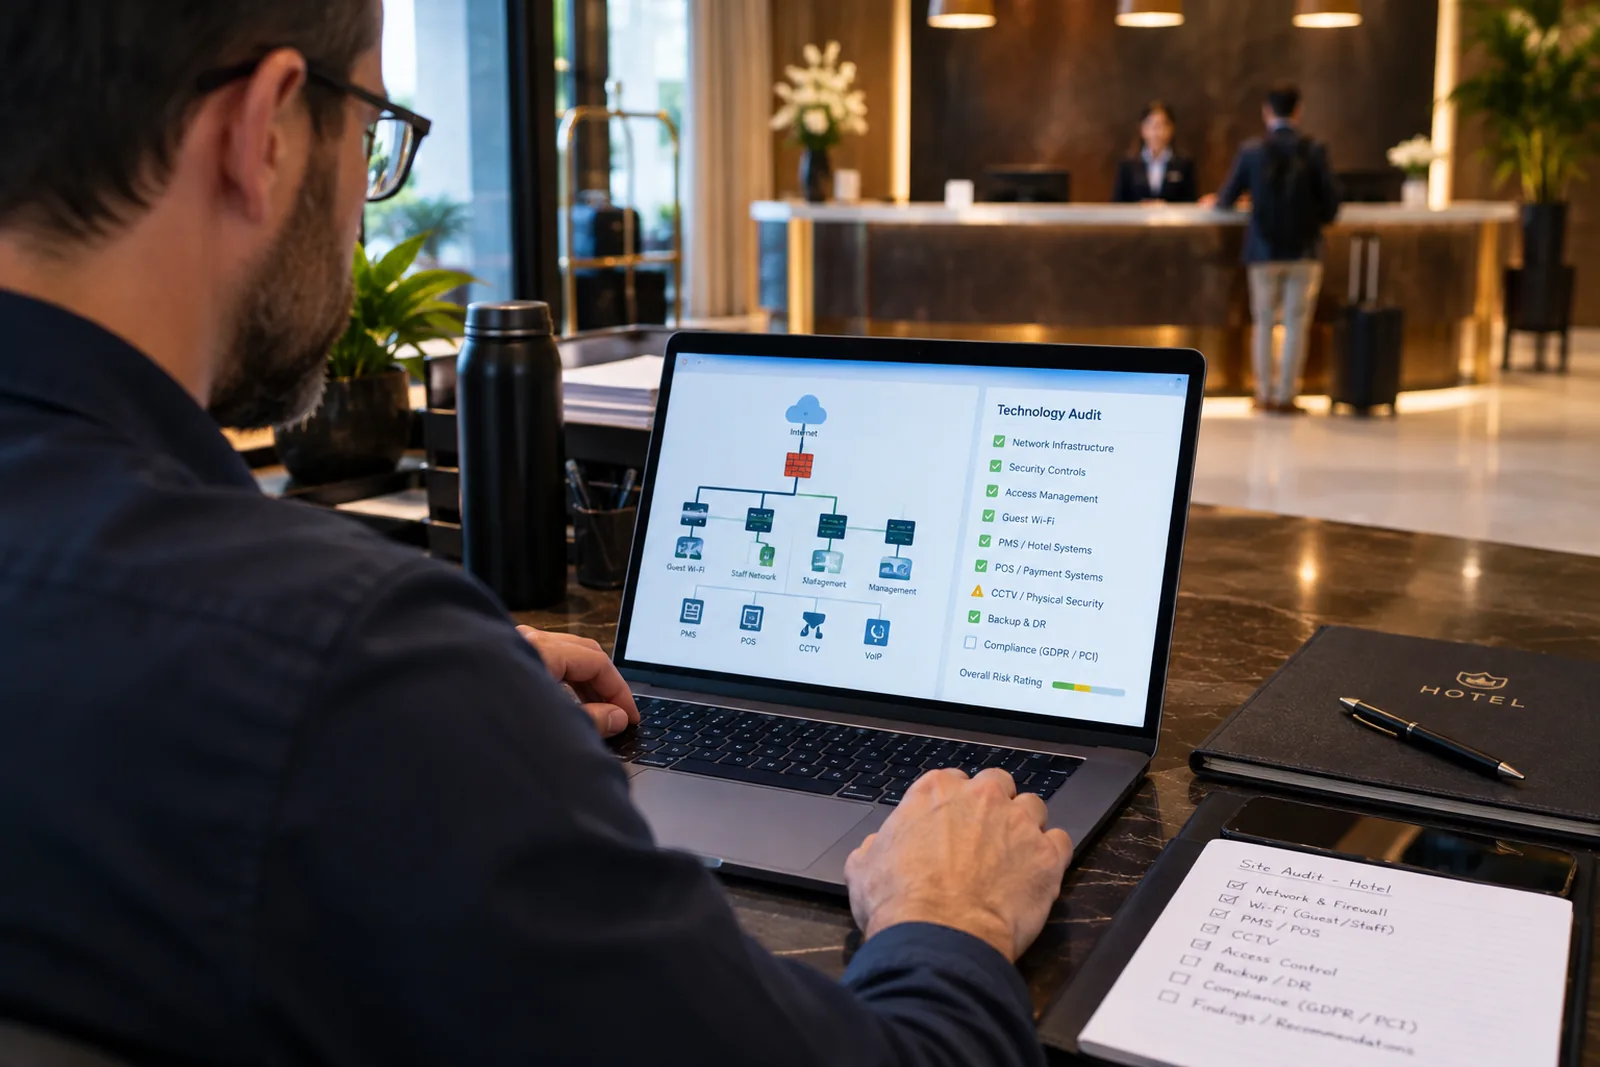
Hotel IT Assessment: A Clear Picture Before You Invest
Before recommending any change, we review the technology across the hotel and the head office: strategy, systems, suppliers, contracts and security. It typically takes 2 to 4 weeks for a single hotel and ends with a report of findings prioritised by impact and an investment roadmap.
What the assessment covers
A complete assessment looks at the operation as a whole, including the head office where there is one, not just the issue that prompted the request. We review the documentation and the team's feedback, then spot-check the key points.
IT strategy and governance
Whether there is a clear IT strategy that supports the business goals, the IT policies and procedures, how IT is run day to day, who is responsible for what, and alignment with the brand's technology standards.
Network standards
Standards for cabling, network segmentation and fault tolerance, checked against the network diagrams. A review of standards, not an in-depth network audit.
Core systems and cloud
PMS, POS, booking engine, channel manager, the cloud services in use and the integrations between them.
Assets, patching and hardening
Hardware and software inventory, licences, patching and system hardening standards.
Access and data
User accounts and permissions, MFA, removal of former staff access, who can access which data and how data is managed.
Security and compliance
Backups tested by actually restoring them, incident response and alignment with the LGPD and, where applicable, PCI DSS.
Guest technology
Guest Wi-Fi, electronic locks, in-room controls, digital check-in and AI tools used in guest service.
Contracts, suppliers and costs
SLAs, costs, renewal dates and the dependency risk of every active supplier, and what the hotel spends on technology compared with what it needs.
When an assessment makes sense
- Before taking over IT management of a new or recently acquired hotel
- When considering a change of PMS, MSP or security supplier
- When IT or hotel technology outages keep recurring
- When IT and hotel technology spending seems too high for what the hotel gets
- Before a renovation or a new build
- After a change in the hotel's leadership
- When there is no clear documentation of the current infrastructure
- Before an LGPD or PCI DSS audit
- Assessment report with findings and risks prioritised by impact
- Complete map of active technology suppliers and contracts
- Short, medium and long-term recommendations
- Initial technology investment roadmap
- Meeting to present the results to management or the board
Why start with an assessment
Technology decisions made without a prior assessment tend to fix the most visible symptom, not the cause. A hotel that replaces its PMS because the current one is slow can end up with the same problem on the next system if the real cause is an undersized network or an inadequate connectivity provider. The assessment exists so that every investment decision, whether replacing a system, engaging a virtual IT manager or reviewing a contract, starts from a complete view of the operation, not an assumption.
How our assessment works
- Initial discovery: a meeting with hotel management and collection of existing documentation, such as policies and procedures, contracts, system and asset inventories and network diagrams, where available.
- Review and spot checks: a review of the documentation and interviews with the team, with spot checks on the key points: IT strategy and governance, network standards, core systems, access, patching, security settings and guest technology.
- Contract and supplier review: assessment of SLAs, costs, renewal dates and dependency risks for every active supplier, and of what the hotel spends on technology compared with what it needs.
- Compliance check: a check of the level of compliance with the LGPD (Brazil's data protection law) and, where applicable, PCI DSS.
- Report and presentation: delivery of the report with findings prioritised by risk and impact, and presentation of the action plan to management or the board.
What we need from your team
Short interviews with the IT and hotel technology teams and some of the department heads, plus the existing documentation. We keep it short and simple, and we don't make any changes to your systems.
Related pages
Frequently asked questions about hotel IT assessments
How is a hotel IT assessment carried out?
In five stages: initial discovery with hotel management, a review of the documentation, standards and core systems with spot checks, a review of active contracts and suppliers, a compliance check against the LGPD and, where applicable, PCI DSS, and a final report with findings prioritised by risk and impact, presented to management or the board.
How do you assess a hotel's IT infrastructure?
By reviewing standards rather than auditing every device: cabling, network segmentation and fault tolerance, checked against the network diagrams, along with the asset inventory and patching and hardening standards, with spot checks on the key points. This is done together with a review of the core systems (PMS, POS, booking engine) and the integrations between them, because undersized infrastructure is often the real cause behind slow or unstable systems.
Are an IT assessment and an IT audit the same thing?
Not exactly. The assessment is a structured review of the technology across the hotel and the head office, with spot checks on the key points, ending with a report of prioritised findings. It is not a formal certification audit: it does not issue a compliance opinion or replace a PCI DSS assessor or an ISO certification. But we look at many of the same controls those audits check, so it is good preparation for them.
How long does a hotel IT assessment take?
Typically 2 to 4 weeks for a single hotel, from the first meeting to the report; chains and multi-property operations take longer. The exact timeline depends on the size of the operation and the number of systems and suppliers involved, and is set out in the scope proposal before any technical work begins.
Does a hotel that already has an MSP or IT manager still need an independent assessment?
Yes. An outside view is more objective than the delivery partner reviewing its own work, and an in-house IT manager may not have the time or distance from the operation to see risks that have built up over time. An independent assessment validates what is being delivered and gives the MSP or IT manager a clear, shared list of priorities.
What does the hotel receive at the end of the IT assessment?
A report with findings and risks prioritised by impact, a complete map of active technology suppliers and contracts, short, medium and long-term recommendations, an initial investment roadmap and a meeting to present the results to management or the board.
How much does a hotel IT or cybersecurity assessment cost?
There is no fixed price, because the scope depends on the size of the hotel: the number of properties, the number of systems and suppliers involved (PMS, POS, booking engine, Wi-Fi, cameras), whether there is an in-house technical team or an MSP to review, and the compliance requirements that apply (LGPD, PCI DSS). The initial discovery with hotel management is enough to propose a scope and timeline, and we then present an investment proposal before any technical work begins.
Ready to see where your hotel's IT stands?
Talk to our team and schedule the initial assessment.